
Cyber Risk Moves Rapidly Up Corporate Agenda but Insurance Uptake Still Lags… Shannon Chamber seminar hears
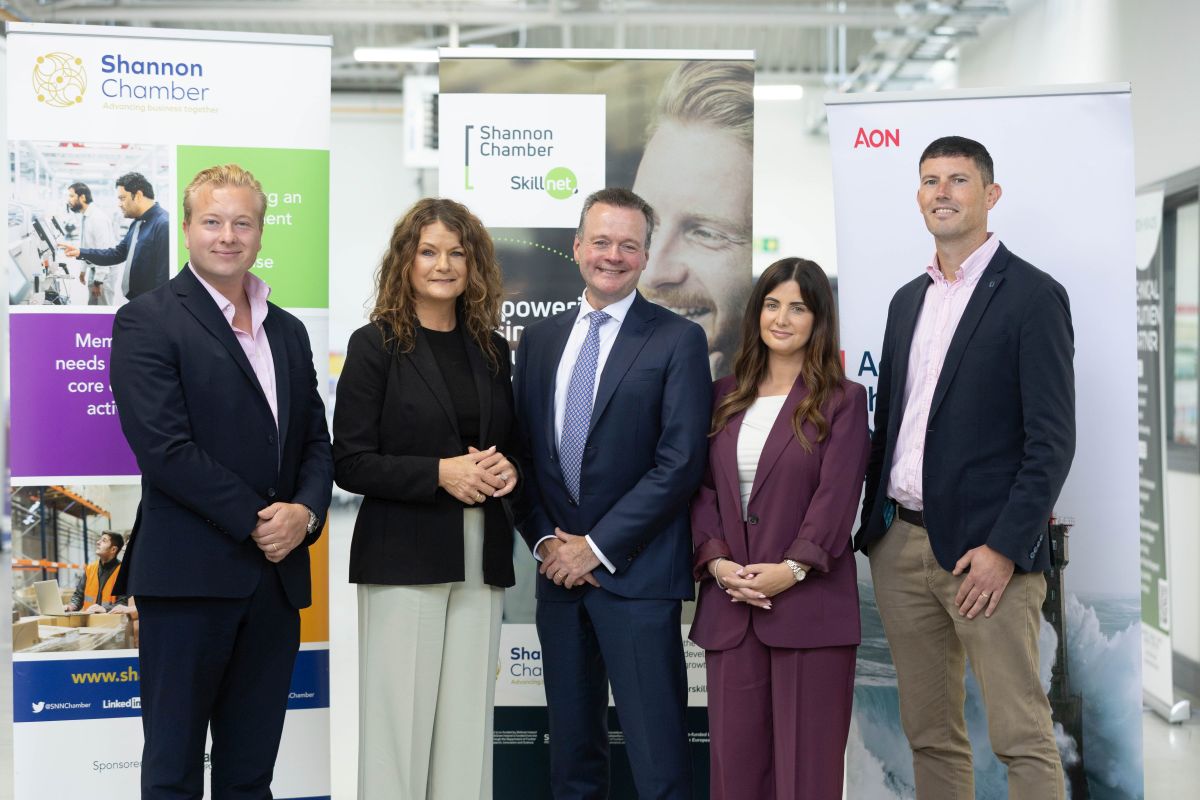
Pictured at the cyber risk seminar (from left): George Suckling, cyber underwriter, Travelers; Helen Downes, CEO, Shannon Chamber; Peter Brady, head of risk capital Aon; Leann Moroney, cyber practice lead, Aon; and Niall O’Grady, head of information systems, The Shannon Airport Group. Photograph by Eamon Ward
Human error, third-party risk, AI-enabled attacks and business interruption among key concerns for organisations and insurers
As cyber risk moves rapidly up the corporate agenda, organisations are recognising that a cyber incident can have consequences far beyond technology alone. Yes, despite the growing awareness, many businesses still do not purchase dedicated cyber insurance.
This protecting gap was a key theme at a recent Shannon Chamber panel discussion on cyber risk, featuring Leann Moroney, cyber practice lead with Aon, George Suckling, cyber underwriter with Travelers, and Niall O’Grady, head of information systems with The Shannon Airport Group. The panel stressed that smaller and medium-sized companies are particularly exposed, often lacking the resources and resilience of larger organisation when a serious incident occurs.
Opening the event, Shannon Chamber CEO Helen Downes, said that cyber risk has evolved beyond an IT issue to a board-level discussion in organisations and that this shift reflects the scale of the potential impact on a business.
“A cyber incident can affect much more than an organisation’s technology. It can interrupt operations, result in direct financial losses, create regulatory obligations and damage an organisation’s reputation,” she said.
In a fast-paced interview-style event, Leann Moroney and the panellists examined the changing threat landscape, the experience of insurers dealing with cyber claims, and the practical steps organisations can take to strengthen their resilience.
Stating that cyber security is no longer regarded simply as an IT responsibility, they stressed that high-profile attacks, increased regulatory requirements, growing dependence on digital systems and supply chains, and the rising frequency of business email compromise and social engineering attacks have all contributed to cyber risk becoming a board-level issue.
One of the strongest messages emerging from the discussion was the growing importance of third-party and supply-chain cyber risk, given that seventy-seven per cent of claims emanate via third parties.
“The risk is not confined to technology providers. Businesses need to identify all suppliers, establish which are critical to continued operations, and carry out appropriate due diligence on those suppliers,” Leann Moroney stated.
A cyber incident affecting a critical operational supplier can create substantial business interruption, particularly where an organisation is dependent on a single source and has no immediate alternative supplier available.
“This is particularly important for manufacturers and businesses with complex supply chains.
“A company may have very strong controls within its own organisation but could still be exposed through a critical supplier. Businesses therefore need to understand not just their own cyber resilience, but the resilience of the organisations on which they depend,” Leann commented.
Business leaders were urged to question how secure and prepared they are for an unexpected cyber event and to assess if they truly understand the potential impact an attack could have on their organisation.
Another stark figure highlighted at the event was that approximately sixty-nine per cent of cyber claims can originate from human error, with business email compromise and social engineering attacks also becoming increasingly frequent
“While organisations continue to invest heavily in technology, people remain a major point of vulnerability,” Niall O’Grady stated.
He also warned businesses to be aware of the impact artificial intelligence, which is making it easier for cybercriminals to produce convincing emails, impersonate trusted individuals and launch attacks at a greater scale.
“Business email compromise is of particular concern. These attacks can involve criminals impersonating senior executives, suppliers or trusted business contacts persuading an employee to change payment details, transfer money or provide access to sensitive information.”
Highly experienced in cyber risk insurance, London-based cyber underwriter George Suckling said that, from an insurer’s perspective, attention is increasingly focused on an organisation’s overall cyber security posture and preparedness rather than simply the volume of data it holds.
“Insurers are looking at factors including the sector in which a company operates, revenue, cyber controls, business continuity arrangements, and the potential impact of operational downtime. Core expectations include offline and encrypted backups, multi-factor authentication for remote access, an incident response plan, a business continuity plan, regular vulnerability scanning and prompt application of critical security patches,” he said.
Stating that cyber insurance covers areas such as the immediate costs of incident response and system restoration, privacy and security liabilities, business interruption losses and cybercrime risks such as social engineering fraud and business email compromise, he emphasised that the value of cyber insurance can extend beyond financial reimbursement.
“When an incident occurs, organisations may need immediate access to forensic specialists, legal advisers, communications expertise and other specialist support. Having these relationships established before an incident can be particularly valuable during the first critical hours,” he stated.
Seminar attendees were advised to test their incident response plans with their technical and senior management teams as exercises of this nature can help clarify who makes key decisions, how the business communicates internally and externally, how operations are maintained, when regulators or customers need to be informed, and how the organisation
They were also advised to speak to their insurers and claims teams before an incident occurs, ensure key insurance information is retained offline, and assess their cyber security against recognised frameworks rather than waiting until a loss occurs.
As Shannon Chamber’s Helen Downes said: “The central message for businesses is preparedness and resilience. No organisation can assume it will never experience a cyber incident. What businesses can control is how well prepared they are, how quickly they can respond, how effectively they can continue operating and how rapidly they can recover.
“Cyber resilience requires leadership, employee awareness, tested processes, strong supplier management, appropriate insurance protection and a clear understanding of what the organisation will do when something goes wrong.
“Recovery periods can vary considerably depending on the organisation, the nature of the attack and the controls already in place, with disruption potentially continuing well beyond the initial restoration of IT systems. Preparedness is essential,” she added.